Hexatic sets up Global Capability Centres in India, keeps organisations protected with managed security and compliance, and designs and runs the IT infrastructure behind them, as one accountable partner.
ISO 27001 & ISO 9001 certified · Pune · Sunnyvale · Europe


Choose the outcome you need.
Entity, hiring, governance and day-to-day operations, run as an extension of your business.
Managed security and compliance that protects you all year, plus VAPT and assessments when you need them.
Design, refresh and run the networks, data centres, cloud and collaboration tools your teams rely on.
Many clients use more than one service, with one accountable team across all of them.
A GRC platform for risk, controls, policies, vendors and audit evidence, covering ISO 27001, SOC 2, GDPR and DPDP.
An ERP for corrugated box manufacturers: costing, production, quality and GST, from paper reel to paid invoice.
One owner app for physical products. Manufacturers get registration, warranty, support and reorders in a single shared app.
One team across your people, security and infrastructure, so nothing falls between vendors.
ISO 27001 and ISO 9001 certified processes for how we build, secure and operate.
Offices in Pune and Sunnyvale, with support for clients in Europe.
Most projects start within 3 to 7 working days of sign-off.
Compliance Platform vs. Spreadsheets: When to Switch? Introduction Compliance management is no longer just about maintaining documents, updating spreadsheets, and preparing evidence before an audit, it has become a daily operational discipline. Organizations must continuously manage risks, monitor controls, review policies, assess vendors, and demonstrate that their compliance activities are operating effectively. For many businesses, […]
Read MoreWe tend to think of phishing as a test of stupidity, a digital filter that only catches careless or tech-illiterate people.
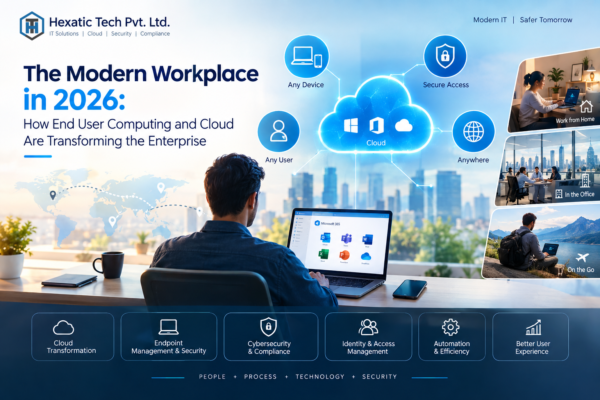
Read MoreThe Modern Workplace in 2026 : How End User Computing and Cloud are Transforming the Enterprise The way employees work has changed dramatically over the last few years. Users are no longer limited to traditional office desktops, corporate networks, or a single workplace location. Today, employees expect secure and seamless access to applications, data, and […]
Read More
Every partnership starts with the right questions. Here's everything you need to know about working with Hexatic, from getting started to the support we bring long after your solution goes live.
Startups, growing companies and enterprises, especially businesses building teams in India and organisations that need strong cybersecurity and compliance, including regulated sectors.
Typically 90 to 120 days from the start of the engagement.
Yes. You can start with a small team and grow the centre as your needs develop.
No. Our cybersecurity and compliance services stand on their own and are available to any organisation, whether or not you work with us on a GCC.
Yes. We map your controls, gather evidence and close gaps. Certification is issued by an accredited auditor, and our ComplyPhi platform can help you manage compliance day to day.
Yes. We often work with internal teams as design, implementation, security or consulting partners rather than replacing them.
For most engagements we can start within 3 to 7 working days after requirements are agreed and commercials are confirmed.
Both. We run 24/7 security monitoring, managed firewall and endpoint security, compliance as a service and managed infrastructure, and also take on one-off work such as VAPT, assessments and infrastructure refreshes.
Contact us through the website and tell us what you need. We will set up a call to understand your goals and suggest a practical next step.
Typically 90 to 120 days from the start of the engagement.
Yes. You can start with a small team and grow the centre as your needs develop.
No. Our cybersecurity and compliance services stand on their own and are available to any organisation, whether or not you work with us on a GCC.
Yes. We map your controls, gather evidence and close gaps. Certification is issued by an accredited auditor, and our ComplyPhi platform can help you manage compliance day to day.
Yes. We often work with internal teams as design, implementation, security or consulting partners rather than replacing them.
For most engagements we can start within 3 to 7 working days after requirements are agreed and commercials are confirmed.
Both. We run 24/7 security monitoring, managed firewall and endpoint security, compliance as a service and managed infrastructure, and also take on one-off work such as VAPT, assessments and infrastructure refreshes.
Contact us through the website and tell us what you need. We will set up a call to understand your goals and suggest a practical next step.